
A wake-up call for data security in the digital age.
In today’s interconnected world, personal data is a valuable asset, making identity theft a growing concern. The Nusapro case is a clear example. Two employees were arrested after stealing thousands of ID card data to meet sales targets. This breach highlights the vulnerabilities in data protection systems, showing how easily personal information can be exploited. The impact of identity theft is not just financial—it can damage lives and reduce trust. Protecting personal data is essential, and both businesses and governments must take responsibility to prevent such violations.
Understanding Identity Theft
Identity theft is no longer an abstract threat—it’s a growing reality in Indonesia. Recent forecasts predict a sharp rise in cybercrimes such as personal data theft in 2024. The 2024 Internet Penetration Survey by the Indonesian Internet Service Providers Association (APJII) paints a concerning picture. With over 8,700 respondents, the survey reveals a significant surge in online fraud and identity theft across the country. Online fraud now accounts for 32.5 percent of cybercrime cases, a drastic jump from 10.3 percent in 2023. Personal data theft has also surged, comprising nearly 21 percent of reported incidents.
These statistics underscore a critical issue—public awareness of data security remains low, even as cybercriminal activities are on the rise. This combination poses a serious threat. The Nusapro case clearly demonstrates how easily identity theft can occur when such vulnerabilities are exploited. As cybercrime evolves, so must our efforts to protect personal information. Preventive measures and cybersecurity education are essential to mitigating these risks. The need for robust data protection has never been more urgent.
Case Analysis: The Nusapro Incident
The Nusapro case serves as a textbook example of how easily identity theft can occur. Under pressure to meet sales targets, two employees stole the personal data of thousands, misusing it to register SIM cards—a clear violation of privacy and trust. The method was alarmingly simple. By using an app designed to autofill NIK data, they exploited a gap in the registration process, allowing them to leverage the stolen personal data to impersonate the identity of any individual without their consent.
The scale of the theft is shocking. Over 3,000 residents of Bogor City had their ID card data compromised. This was not a minor breach but a significant violation of privacy, with serious consequences for those affected. The two malicious actors earned over IDR 25.6 million from their illegal activities, though the true cost is far greater. Victims of identity theft often face long-term difficulties, ranging from financial loss to legal complications.
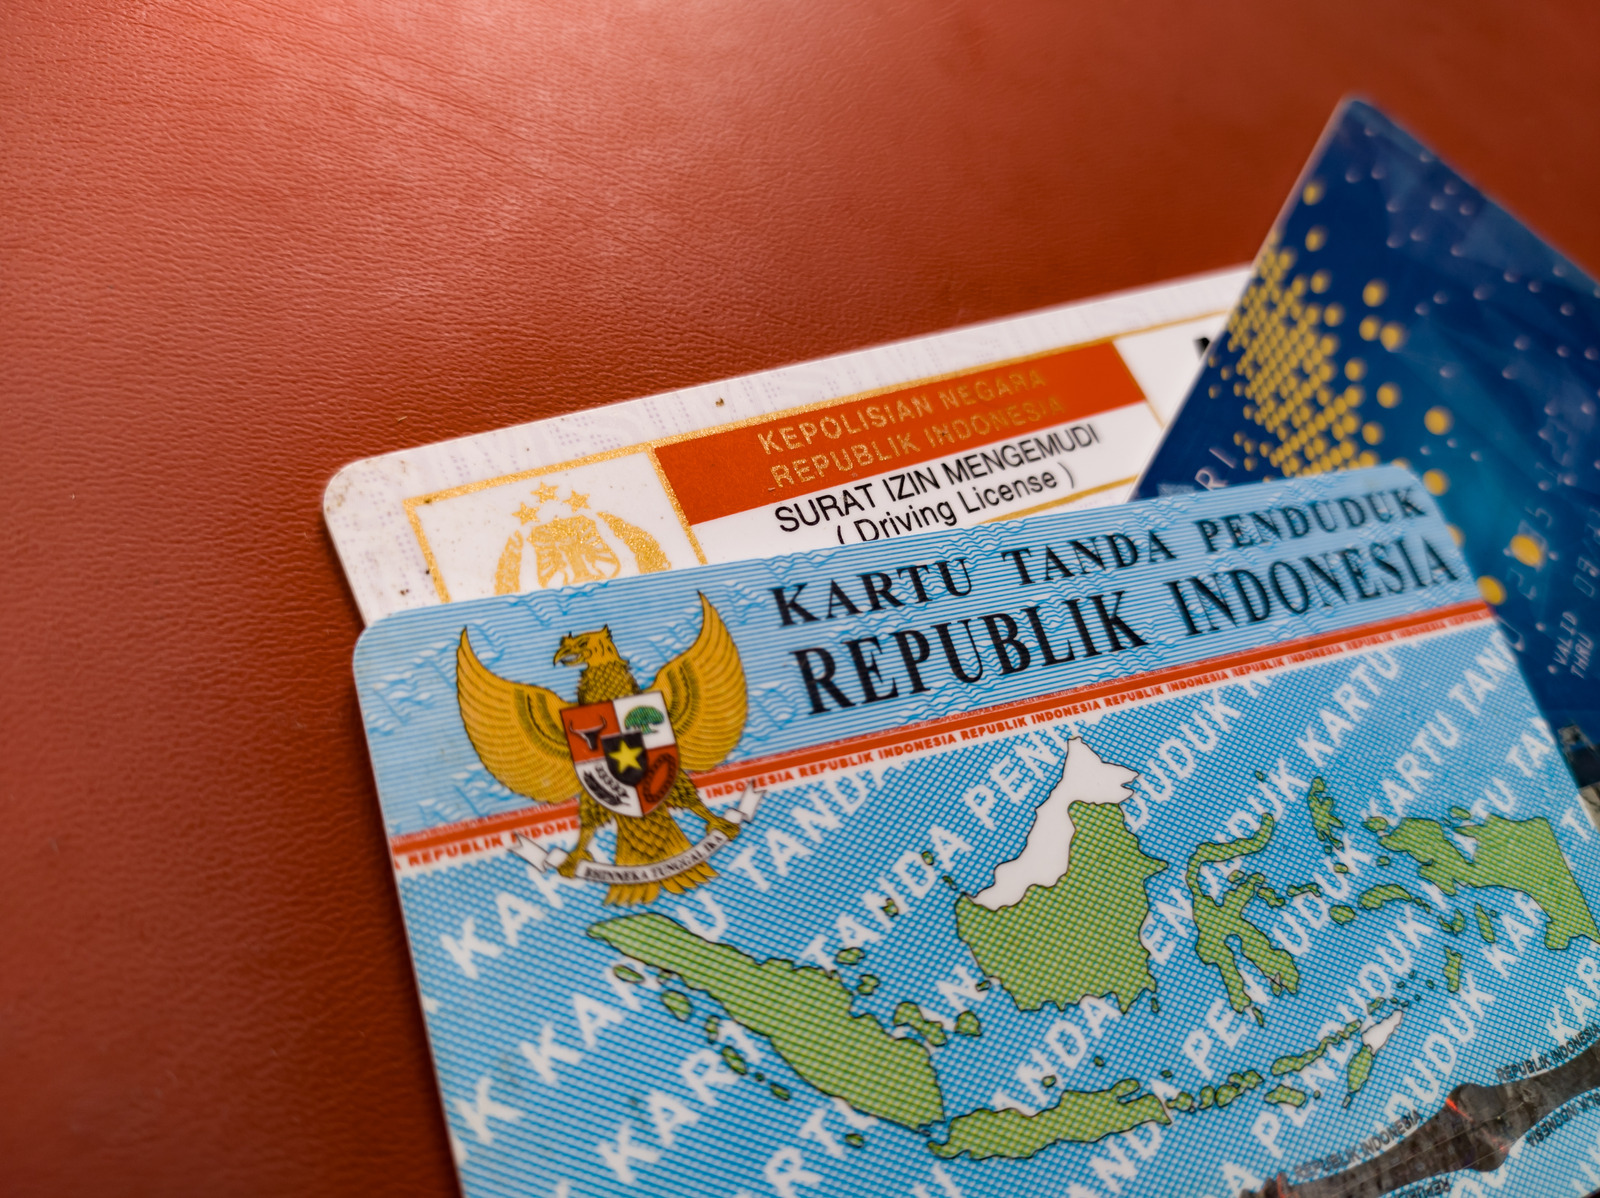
The Nusapro incident highlights a critical issue beyond corporate negligence—it underscores the government’s responsibility. Adequate data protection measures for ID card data are crucial, yet government institutions have repeatedly failed in this regard. This breach is just one of many instances where personal data from government sources has been compromised. It is evident that stronger governmental safeguards are needed to prevent such breaches and protect the personally identifiable information of the citizens.
The Role of Organisations in Preventing Identity Theft
Organisations play a crucial role in preventing identity theft. It’s not just about regulatory compliance; it’s about earning and maintaining trust. Implementing robust data protection measures is essential. Secure data storage, strict access controls, and regular audits can help prevent unauthorised access and misuse of personal information.
Vendor management is also critical. Companies must ensure that their partners adhere to high data protection standards. The Nusapro case underscores the dangers of inadequate due diligence. Partners should be thoroughly vetted to ensure their practices align with security and privacy policies.
Consumer education is equally important. Businesses should inform customers about data protection and provide guidance on what to do if their information is compromised. Clear communication can significantly help in mitigating risks.
Moreover, while organisations must lead in data protection, the government also needs to improve its cybersecurity practices. Frequent breaches of government-held data highlight the urgent need for better protections and more stringent enforcement. Enhanced government measures are crucial for safeguarding citizens’ personal information and supporting overall data security.
Preventing identity theft requires a collaborative approach from both parties. Organisations must implement robust security measures, while the government must strengthen its data protection practices to address ongoing vulnerabilities.
Legal and Regulatory Implications
Data protection laws impose severe consequences for breaches, affecting both companies and individuals. Companies like Nusapro can face substantial administrative sanctions, including written warnings, temporary suspension of data processing, deletion of personal data, and fines. According to the Indonesian Personal Data Protection Law (UU PDP), administrative fines can reach up to 2 percent of the company’s annual revenue related to the violation.
On the individual front, criminal provisions are equally stringent. The malicious actors in the Nusapro case face up to 5 years in prison under Indonesian law. UU PDP stipulates that anyone who unlawfully obtains or collects personal data with the intent to benefit themselves or others, causing potential harm to the data subject, can be sentenced to up to 5 years in prison and/or fined up to IDR 5,000,000,000 (five billion rupiah).
Recommendations for Businesses
- Data Security Measures: Businesses should implement comprehensive data protection systems, including encryption, secure access controls, and data loss prevention. These measures are crucial for safeguarding against unauthorised access and data breaches.
- Regular Risk Assessments: Regularly evaluate and update security protocols to address emerging vulnerabilities. This should include security penetration testing and vulnerability assessments to identify weaknesses before they can be exploited.
- Employee Training: Employees must be well-informed about data protection practices and potential threats. Regular training sessions can help prevent accidental breaches and foster a culture of security awareness.
- Monitor Partner Compliance: Businesses should enforce strict data protection standards with all partners. Regular audits and due diligence are necessary to ensure that partners adhere to the same security measures as the organisation.
Recommendations for Indonesian Government
- Accelerate PDP Framework Development: The Indonesian government is in the process of establishing a PDP regulatory body, finalising the PDP regulatory body government regulation, and completing the PDP Government Regulation (PP PDP). These efforts must be expedited to set clear data protection standards and ensure compliance across all sectors.
- Improve Cybersecurity Practices: Invest in advanced cybersecurity infrastructure and strategies to safeguard government-held data. Regular updates and testing of these systems are essential to protect against evolving cyber threats.
- Promote Public Awareness: Launch educational campaigns to inform the public about data protection and their rights. Raising awareness will empower individuals to better protect their personal information and recognise potential threats.
Conclusion
The Nusapro case underscores the urgent need for robust data protection measures from both businesses and governments. This incident exposes the serious consequences of inadequate data security and highlights the critical roles that organisations and regulatory bodies must play in safeguarding personal information.
Businesses must take immediate action to strengthen their data protection practices. Implementing robust security measures, conducting regular risk assessments, and ensuring strict compliance with data protection laws are essential steps to prevent data breaches. Additionally, they should monitor partners to ensure the same high standards of security are maintained.
Governments play a crucial role in setting and enforcing data protection regulations. The ongoing efforts to establish a Personal Data Protection (PDP) institution, finalise the PDP regulatory body government regulation, and complete the PDP Government Regulation (PP PDP) must be expedited. These measures are essential for establishing clear data protection standards and ensuring comprehensive compliance across all sectors.
In summary, both businesses and governments must prioritise data protection to prevent incidents like the Nusapro case. By reinforcing security measures and regulatory frameworks, we can better safeguard personal data and uphold trust in our digital systems.
References:
At Cybe, we understand the complexities of data protection and cybersecurity, and we’re here to help businesses stay ahead of emerging threats.
Our Data Privacy Advisory provides expert consultation on regulatory compliance, policy development, and incident response planning, ensuring your business is fully prepared to meet today’s data protection challenges.
Through our Cyber Skills Academy, in partnership with Macquarie University, we offer specialised education and courses that equip your team with the knowledge to protect sensitive data.
For hands-on security, our Security Assurance Testing leverages the latest tools and techniques to conduct thorough penetration testing and in-depth vulnerability assessments.
Contact us today to strengthen your security posture and safeguard your business against future threats.